Google Workspace Administrator (GCX)
Virtualization, Google
This course delivers a structured overview of administering and securing Google Workspace, focusing on configuring security policies, using the Admin Console and applying Audit logs with the Investigation Tool for forensic analysis of Gmail, Drive and login activity.
It covers practical prevention and response: enforcing MFA/2SV, DLP rules for Gmail and Drive, configuring SPF/DKIM/DMARC and Context-Aware Access, integrating with SIEMs and automating tasks via Admin SDK, APIs and GAM for incident reporting and audits.
THIS TRAINING COURSE WILL HELP YOU:
- Configure Workspace security policies (MFA, DLP, sharing, alerts)
- Investigate incidents: build timelines and identify attacker activity
- Use Admin Console, audit logs and APIs for forensic analysis
- Design prevention processes: user training, sharing limits, automation
WHO SHOULD ATTEND?
- Google Workspace administrators and security specialists
- IT and helpdesk teams at companies migrating to SaaS
- Auditors, consultants and SOC analysts handling cloud incidents
COURSE LOCATION AND AVAILABLE DATES
Need this course in English?
Public courses are usually delivered in Czech, but this course is also available in English. We can arrange private training for your team online, at your premises or in our classrooms, and tailor the content to your needs.
For groups of around 4 or more participants, private training can already be comparable in price to booking individual places on a public course. Send us your requirements and we’ll recommend the best format and provide an exact quote.
Request training in English
Course content:
Hide details
-
Introduction to Google Workspace and SaaS security
-
Shared Responsibility Model — responsibilities of Google vs. the customer
-
Roles and org structure (Org Units, Groups, Access Groups)
-
Licenses and editions (Business / Enterprise) and security implications
-
Typical threats (phishing, public links, auto-forwarding, OAuth)
-
Admin Console and Audit logs
-
Key Admin Console areas (Alert Center, Security Rules)
-
Working with Email Log Search, Drive Audit, Login Activity
-
Investigation Tool (Enterprise) — building queries and exporting results
-
Exporting logs (CSV, Reports API, BigQuery) and offline analysis
-
Forensic analysis — practical case study
-
Data exfiltration and email forwarding incidents
-
Downloading and analysing logs (Drive, Email, Login)
-
Creating an attack timeline — attacker steps and stolen files
-
Remediation steps (password resets, MFA, removing forwards)
-
Structuring reports and communicating with management
-
Security policies and data loss prevention
-
MFA / 2SV and SSO integration (Azure AD, Okta)
-
DLP rules for Gmail and Drive
-
Sharing settings (internal, public, domain allow/block lists)
-
SPF / DKIM / DMARC and anti‑phishing policies
-
Context-Aware Access — restrict by IP, device, geolocation
-
Alerting (webhooks, email, Chat notifications)
-
Automation and integration
-
Admin SDK, Reports API, Directory API
-
GAMADV‑XTD3 — exporting logs, auditing sharing, changing forwards
-
Apps Script / Cloud Functions for scheduled audits
-
SIEM integration (Chronicle, Splunk, ELK)
-
Connecting to ticketing systems (Jira, ServiceNow)
-
Best practices and security checklist
-
Incident Response Playbook (detect → contain → recover)
-
Communication plan and documentation (reports, logs, chain of custody)
-
Tabletop exercises, sharing audits, phishing tests
-
Quick admin checklist (daily / weekly / monthly controls)
-
Bonus (if time allows)
-
Compliance (GDPR, ISO 27001, SOC 2)
-
Auditing OAuth apps and restricting app access
-
Chronicle SIEM mini-lab — ingesting logs and creating detections
-
Prerequisites:
-
Basic Google Workspace user knowledge; admin experience with SaaS is a plus.
-
Schedule:
-
2 days (9:00-17:00)
Training and learning environment
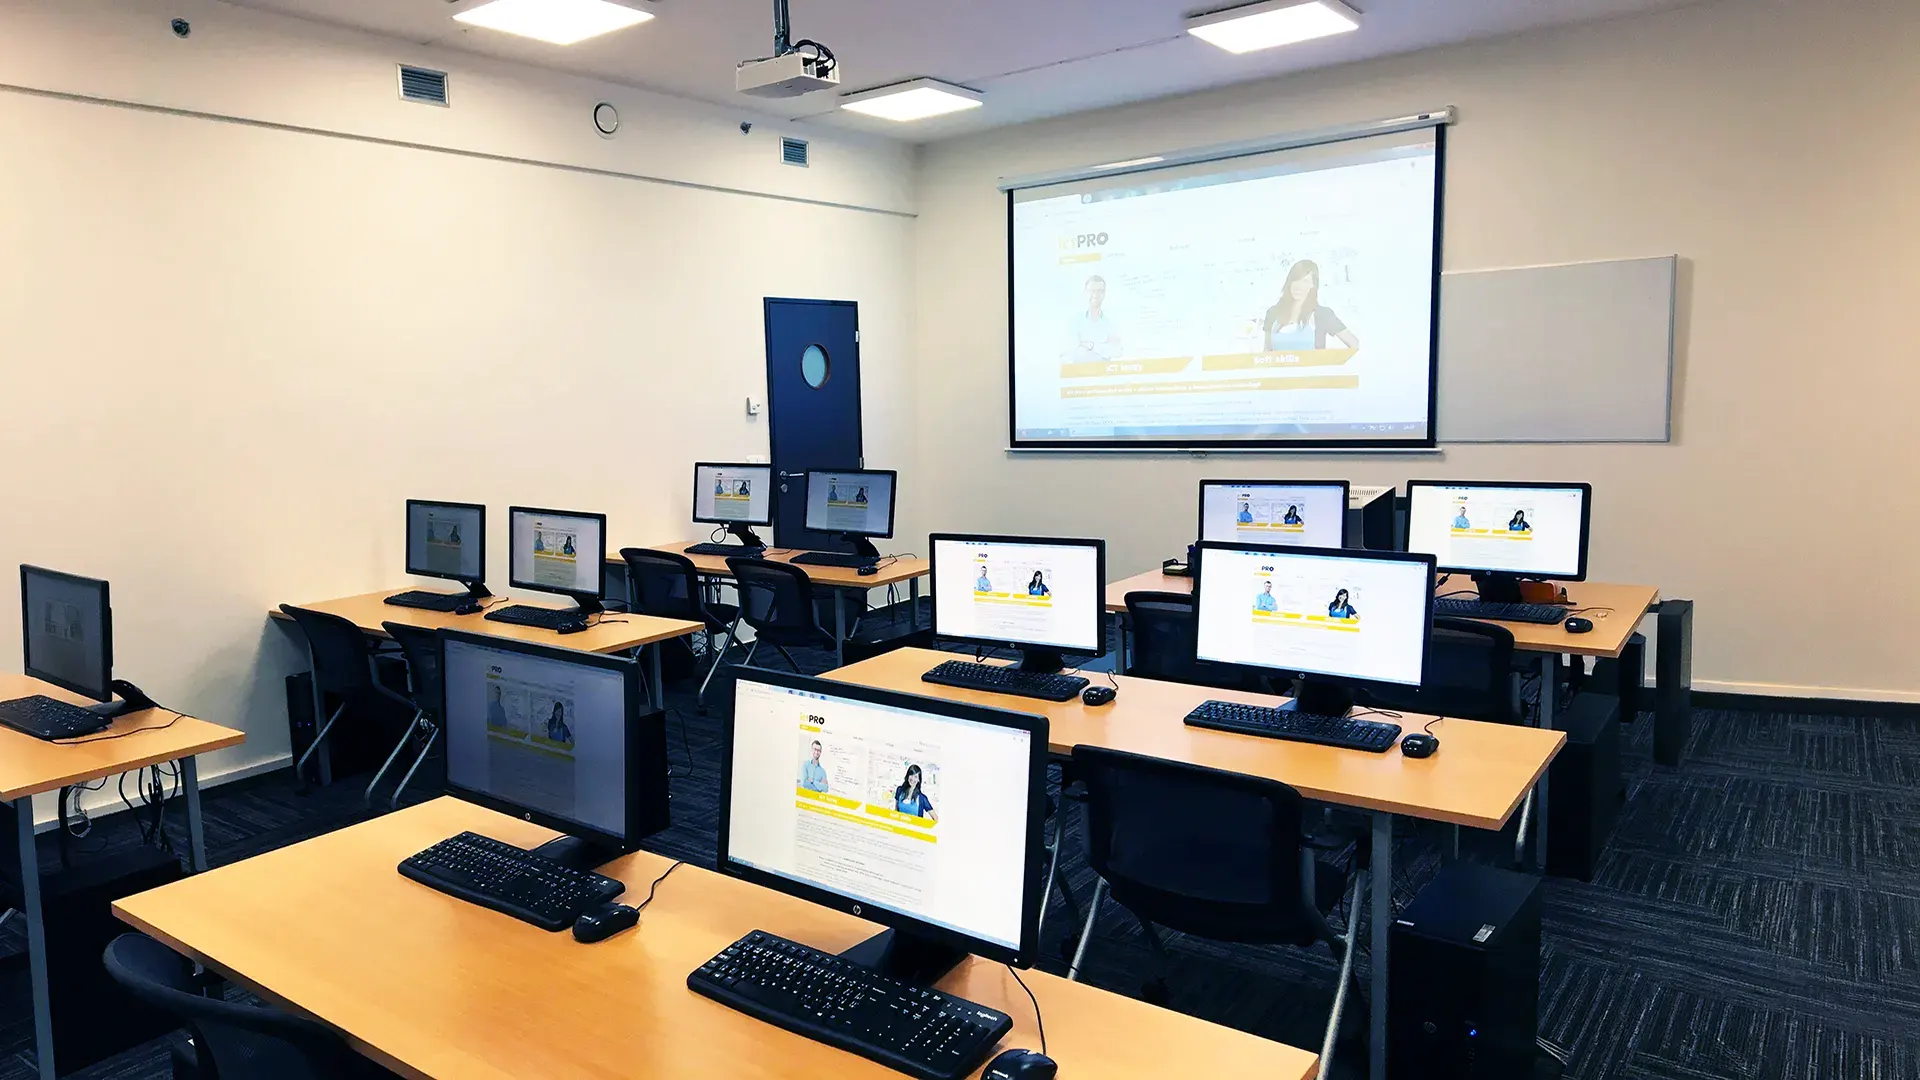 What does the environment for in-person IT courses look like?We hold training courses in our own classrooms equipped with modern computer equipment for each participant and a large projection screen. Each workstation is fitted with a powerful computer for seamless practical exercises, and the environment supports a calm, friendly atmosphere during training.
 Do I need to bring my own laptop to the classroom IT course?Our training rooms are fully equipped, so you do not need to bring your own laptop. A modern computer with all necessary hardware and software is ready for you at your workstation.
 Will you receive an official certificate after completing an IT course?Yes, upon successful completion of the training course, you will receive an official ICT Pro certificate confirming your participation and acquired technical skills. You can use it to verify your qualifications or add it to your professional profile.
 Where can you find our training center in Brno?The premises of the ICT Pro training center are located on the 1st floor of the COMGUARD building at Sochorova 38 in Brno. Positioned on the border of Žabovřesky and Komín, the location is easily accessible by both car and public transport.
 Where can you find our training center in Prague?The premises of the ICT Pro training center are located on the 1st floor of the Opatov Park building at Líbalova 1, Prague 11 – Chodov. The location provides a comfortable environment for your education with convenient access.
 What facilities and refreshments are available to you during training breaks?Our training centers feature a fully equipped kitchenette for a comfortable break during your courses. The facilities include a coffee machine, microwave, kettle, and a wide selection of drinks and snacks.
 What beverage refreshments are available during your course?A beverage station with a coffee machine, teas, syrups, and water is at your disposal throughout the entire training session. You can enjoy a coffee or another drink of your choice anytime during breaks.
 What light refreshments are provided for you during the courses?During course breaks, participants can enjoy light sweet snacks, pastries, and fruit syrups to mix their own drinks. Fresh water dispenser and plates are also available for your convenience.
 Should I bring my own snacks to ICT Pro training?There is no need to. A wide selection of savory snacks, sweet biscuits, and snack bars is available for you during breaks. Boost your energy for all-day focus right inside the training center premises.
 Can you spend training breaks in the fresh air?Yes, an outdoor terrace is available at our training center. During breaks between learning sessions, you can relax in the fresh air in a pleasant green environment.
 Where can you relax during course breaks?Our training center features a spacious outdoor terrace with seating options. During breaks between learning sessions, you can step outside to relax and recharge in the fresh air.