Windows Server – PKI Deployment and Management (PKI)
Cybersecurity, ICT Security
The PKI – Electronic Signatures in Practice for Administrators course is designed for system administrators and anyone interested in secure communication over the Internet and LAN networks. During the training, participants will learn to make full use of standard PKI mechanisms available in Windows Server and MS Office applications.
All topics are covered primarily through practical laboratory exercises. Participants will learn to work with certificates on client systems and master the fundamentals of certification authority administration.
THIS TRAINING COURSE WILL HELP YOU:
- Gain practical skills in PKI and electronic signature administration
- Understand the principles and importance of PKI
- Learn to install, configure and manage certification authorities using Windows Server services
WHO SHOULD ATTEND?
- System and network administrators involved in securing communications
- Professionals using PKI in Windows environments
- Anyone interested in secure management of certificates and electronic signatures
COURSE LOCATION AND AVAILABLE DATES
Need this course in English?
Public courses are usually delivered in Czech, but this course is also available in English. We can arrange private training for your team online, at your premises or in our classrooms, and tailor the content to your needs.
For groups of around 4 or more participants, private training can already be comparable in price to booking individual places on a public course. Send us your requirements and we’ll recommend the best format and provide an exact quote.
Request training in English
Public course on a related topic
Course content:
Hide details
-
Cryptography, Certificates and PKI Principles
-
Basic cryptographic principles used in Windows environments
-
Symmetric and asymmetric encryption
-
Electronic signatures
-
Hash functions
-
Trust principles in Public Key Infrastructure
-
Digital certificates and their structure
-
Chain of trust and certificate validation
-
Certificate types and their uses
-
Key Usage and Extended Key Usage (EKU)
-
Subject Alternative Name (SAN)
-
CryptoAPI and Cryptographic Service Providers (CSP)
-
Cryptography API: Next Generation (CNG)
-
Key Storage Providers (KSP)
-
Private key security
-
Certificate lifecycle
-
Current state of post-quantum cryptography in Windows Server 2025
-
Support, requirements and limitations of post-quantum algorithms, especially ML-DSA, in AD CS
-
Enterprise PKI Design
-
Certification authority hierarchy design
-
Root CA and Subordinate CA
-
Enterprise CA and Standalone CA
-
Online and offline certification authorities
-
Separation of root and issuing certification authorities
-
Design of a secure and manageable PKI infrastructure
-
Certification authority lifecycle planning
-
Protection of certification authority private keys
-
Use of HSM modules
-
Planning PKI availability, recovery and long-term management
-
Active Directory Certificate Services Deployment and Management
-
Installing Active Directory Certificate Services
-
Configuring the certification authority
-
CA administration and maintenance
-
Certificate Templates
-
Designing and modifying certificate templates
-
Template permissions
-
Defining the purpose of issued certificates
-
Secure certificate issuance for users and computers
-
Manual certificate issuance and management
-
certreq and certutil tools
-
Importing and exporting certificates and private keys
-
Automated certificate issuance
-
Group Policy and autoenrollment
-
Autoenrollment for computers and users
-
Certificate revocation management
-
Certificate Revocation List (CRL)
-
Authority Information Access (AIA)
-
Certificate validity checking
-
Online Responder and OCSP
-
Certification authority backup and recovery
-
Backing up the certificate database and private keys
-
Modern Enrollment and Certificate Issuance Automation
-
SCEP and Network Device Enrollment Service (NDES)
-
Automated enrollment scenarios
-
Issuing certificates to devices and services
-
Overview of the ACME protocol
-
Overview of the EST protocol
-
Options and limitations for their use in Microsoft Windows and AD CS environments
-
Selecting the appropriate enrollment mechanism for the device or service type
-
Practical PKI Applications
-
TLS certificates and their deployment
-
Certificates for Internet Information Services (IIS)
-
Certificates for Remote Desktop Services and RDP
-
Using certificates with other server services
-
TLS hardening
-
Secure configuration of supported protocols and ciphers
-
Certificate pinning
-
Overview of TLS attacks and protective measures
-
Using certificates to authenticate IPsec communications
-
Certificate-based user and computer authentication
-
Encrypting File System (EFS)
-
Centralized EFS configuration using Group Policy
-
EFS key management
-
Data Recovery Agent and recovery scenarios
-
S/MIME
-
Electronic signing and encryption of email messages
-
Certificate management in email scenarios
-
Using PKI in Exchange and other enterprise services
-
Active Directory Certificate Services Security
-
AD CS security model
-
Protecting certification authorities and their private keys
-
Secure Certificate Templates configuration
-
Risks of improperly configured template permissions
-
Risks of uncontrolled enrollment
-
Certificate-based attacks against Active Directory
-
Overview of attacks known as ESC1–ESC15
-
Typical configuration errors enabling privilege escalation
-
Using certificates to authenticate and take over identities
-
Auditing Active Directory Certificate Services environments
-
Monitoring certificate issuance and use
-
Detecting suspicious enrollment
-
AD CS hardening
-
Practical security assessment of deployed PKI
-
Verifying configuration using laboratory scenarios
-
Prerequisites:
-
Knowledge of working with Windows or Linux operating systems. Basic understanding of security in TCP/IP networks.
-
Schedule:
-
3 days (9:00-17:00)
Training and learning environment
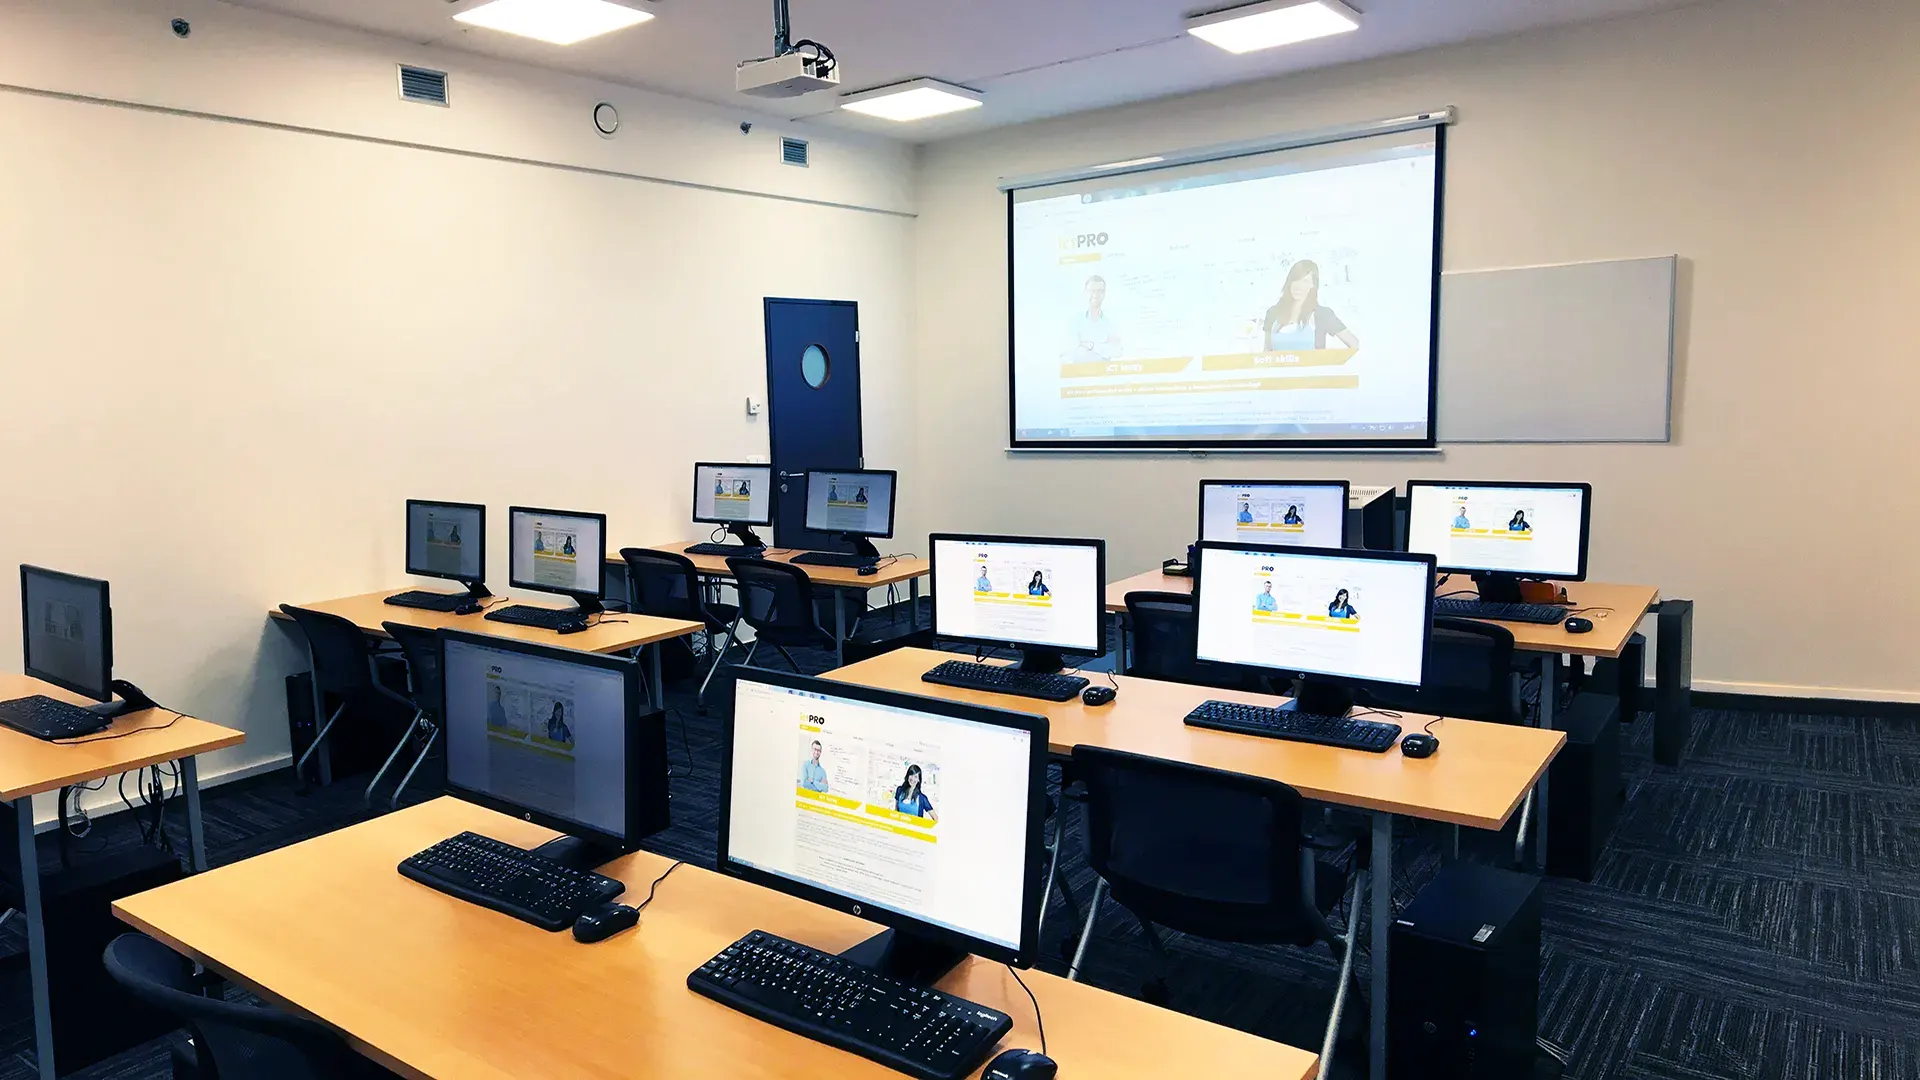 What does the environment for in-person IT courses look like?We hold training courses in our own classrooms equipped with modern computer equipment for each participant and a large projection screen. Each workstation is fitted with a powerful computer for seamless practical exercises, and the environment supports a calm, friendly atmosphere during training.
 Do I need to bring my own laptop to the classroom IT course?Our training rooms are fully equipped, so you do not need to bring your own laptop. A modern computer with all necessary hardware and software is ready for you at your workstation.
 Will you receive an official certificate after completing an IT course?Yes, upon successful completion of the training course, you will receive an official ICT Pro certificate confirming your participation and acquired technical skills. You can use it to verify your qualifications or add it to your professional profile.
 Where can you find our training center in Brno?The premises of the ICT Pro training center are located on the 1st floor of the COMGUARD building at Sochorova 38 in Brno. Positioned on the border of Žabovřesky and Komín, the location is easily accessible by both car and public transport.
 Where can you find our training center in Prague?The premises of the ICT Pro training center are located on the 1st floor of the Opatov Park building at Líbalova 1, Prague 11 – Chodov. The location provides a comfortable environment for your education with convenient access.
 What facilities and refreshments are available to you during training breaks?Our training centers feature a fully equipped kitchenette for a comfortable break during your courses. The facilities include a coffee machine, microwave, kettle, and a wide selection of drinks and snacks.
 What beverage refreshments are available during your course?A beverage station with a coffee machine, teas, syrups, and water is at your disposal throughout the entire training session. You can enjoy a coffee or another drink of your choice anytime during breaks.
 What light refreshments are provided for you during the courses?During course breaks, participants can enjoy light sweet snacks, pastries, and fruit syrups to mix their own drinks. Fresh water dispenser and plates are also available for your convenience.
 Should I bring my own snacks to ICT Pro training?There is no need to. A wide selection of savory snacks, sweet biscuits, and snack bars is available for you during breaks. Boost your energy for all-day focus right inside the training center premises.
 Can you spend training breaks in the fresh air?Yes, an outdoor terrace is available at our training center. During breaks between learning sessions, you can relax in the fresh air in a pleasant green environment.
 Where can you relax during course breaks?Our training center features a spacious outdoor terrace with seating options. During breaks between learning sessions, you can step outside to relax and recharge in the fresh air.